
Quiz
NSE 4 2da
Create a free account to finish this quiz
Save your progress and see your final score.
Already have an account? Sign in
Questions in this quiz (30)
1Refer to the exhibit to view the authentication rule configuration In this scenario, which statement is true?
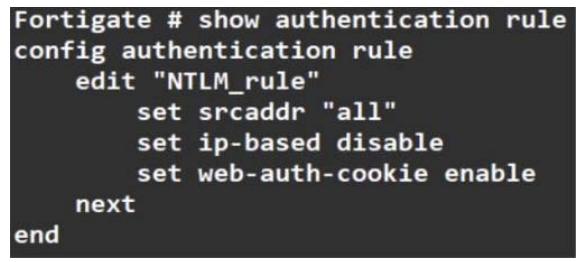
- AIP-based authentication is enabled
- BRoute-based authentication is enabled
- CSession-based authentication is enabled.
- DPolicy-based authentication is enabled
2Which of the following statements correctly describes FortiGates route lookup behavior when
searching for a suitable gateway? (Choose two)- ALookup is done on the first packet from the session originator
- BLookup is done on the last packet sent from the responder
- CLookup is done on every packet, regardless of direction
- DLookup is done on the trust reply packet from the responder
3Which two policies must be configured to allow traffic on a policy-based next-generation firewall
(NGFW) FortiGate? (Choose two.)- AFirewall policy
- BPolicy rule
- CSecurity policy
- DSSL inspection and authentication polic
4Which three CLI commands can you use to troubleshoot Layer 3 issues if the issue is in neither the
physical layer nor the link layer? (Choose three.)- Adiagnose sys top
- Bexecute ping
- Cexecute traceroute
- Ddiagnose sniffer packet any
- Eget system arp
5Which two statements about IPsec authentication on FortiGate are correct? (Choose two.)
- AFor a stronger authentication, you can also enable extended authentication (XAuth) to request the remote peer to provide a username and password
- BFortiGate supports pre-shared key and signature as authentication methods.
- CEnabling XAuth results in a faster authentication because fewer packets are exchanged.
- DA certificate is not required on the remote peer when you set the signature as the authentication method.
6Which of the following are valid actions for FortiGuard category based filter in a web filter profile ui proxy-based inspection mode? (Choose two.)
- AWarning
- BExempt
- CAllow
- DLearn
7Refer to the exhibit, which contains a session diagnostic output.
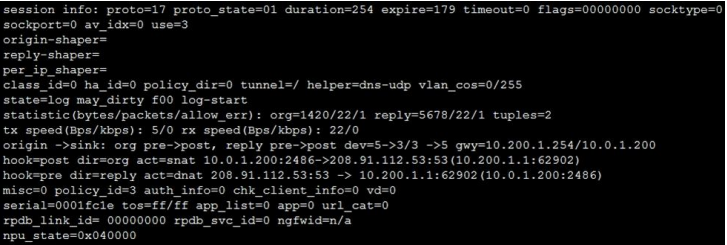
- AThe session is a UDP unidirectional state.
- BThe session is in TCP ESTABLISHED state.
- CThe session is a bidirectional UDP connection.
- DThe session is a bidirectional TCP connection.
8Which two statements are true about collector agent standard access mode? (Choose two.)
A. Standard mode uses Windows convention-NetBios: Domain\Username.- AStandard mode uses Windows convention-NetBios: Domain\Username.
- BStandard mode security profiles apply to organizational units (OU).
- CStandard mode security profiles apply to user groups.
- DStandard access mode supports nested groups.
9Which two VDOMs are the default VDOMs created when FortiGate is set up in split VDOM mode? (Choose two.)
- AFG-traffic
- BMgmt
- CFG-Mgmt
- DRoot
10An administrator needs to increase network bandwidth and provide redundancy.
What interface type must the administrator select to bind multiple FortiGate interfaces?- AVLAN interface
- BSoftware Switch interface
- CAggregate interface
- DRedundant interfac
11Which CLI command will display sessions both from client to the proxy and from the proxy to the
servers?- Adiagnose wad session list
- Bdiagnose wad session list | grep hook-pre&&hook-out
- Cdiagnose wad session list | grep hook=pre&&hook=out
- Ddiagnose wad session list | grep "hook=pre"&"hook=out"
1272.Which three criteria can a FortiGate use to look for a matching firewall policy to process traffic?
(Choose three.)- ASource defined as Internet Services in the firewall policy.
- BDestination defined as Internet Services in the firewall policy.
- CHighest to lowest priority defined in the firewall policy.
- DServices defined in the firewall policy.
- ELowest to highest policy ID number.
13Which statements best describe auto discovery VPN (ADVPN). (Choose two.)
- AIt requires the use of dynamic routing protocols so that spokes can learn the routes to other spokes.
- BADVPN is only supported with IKEv2.
- CTunnels are negotiated dynamically between spokes.
- DEvery spoke requires a static tunnel to be configured to other spokes so that phase 1 and phase 2 proposals are defined in advance.
14An administrator observes that the port1 interface cannot be configured with an IP address.
What can be the reasons for that? (Choose three.)- AThe interface has been configured for one-arm sniffer.
- BThe interface is a member of a virtual wire pair.
- CThe operation mode is transparent.
- DThe interface is a member of a zone.
- ECaptive portal is enabled in the interface.
15NGFW mode allows policy-based configuration for most inspection rules.
Which security profile’s configuration does not change when you enable policy-based inspection?- AWeb filtering
- BAntivirus
- CWeb proxy
- DApplication control
16An administrator created a static route for Amazon Web Services.
What CLI command must the administrator use to view the route?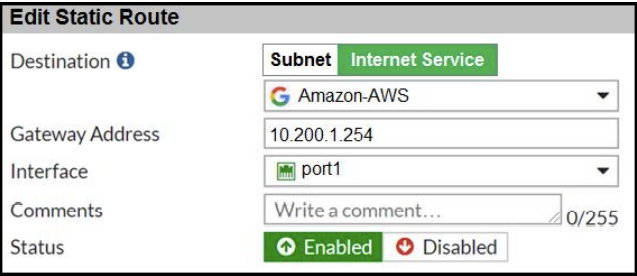
- Aget router info routing-table all
- Bget internet service route list
- Cget router info routing-table database
- Ddiagnose firewall proute list
17Refer to the exhibit to view the application control profile.
Based on the configuration, what will happen to Apple FaceTime?- AApple FaceTime will be blocked, based on the Excessive-Bandwidth filter configuration
- BApple FaceTime will be allowed, based on the Apple filter configuration.
- CApple FaceTime will be allowed only if the filter in Application and Filter Overrides is set to Learn
- DApple FaceTime will be allowed, based on the Categories configuration.
18Examine the following web filtering log.
Which statement about the log message is true?
- AThe action for the category Games is set to block.
- BThe usage quota for the IP address 10.0.1.10 has expired
- CThe name of the applied web filter profile is default.
- DThe web site miniclip.com matches a static URL filter whose action is set to Warning.
19You have enabled logging on your FortiGate device for Event logs and all Security logs, and you have set up logging to use the FortiGate local disk.
What is the default behavior when the local disk is full?- ALogs are overwritten and the only warning is issued when log disk usage reaches the threshold of
95% - BNo new log is recorded until you manually clear logs from the local disk.
- CLogs are overwritten and the first warning is issued when log disk usage reaches the threshold of 75%
- DNo new log is recorded after the warning is issued when log disk usage reaches the threshold of 95%
- ALogs are overwritten and the only warning is issued when log disk usage reaches the threshold of
20A network administrator has enabled full SSL inspection and web filtering on FortiGate. When visiting any HTTPS websites, the browser reports certificate warning errors. When visiting HTTP websites, the browser does not report errors.
What is the reason for the certificate warning errors?- AThe browser requires a software update.
- BFortiGate does not support full SSL inspection when web filtering is enabled.
- CThe CA certificate set on the SSL/SSH inspection profile has not been imported into the browser.
- DThere are network connectivity issues
21What is the limitation of using a URL list and application control on the same firewall policy, in NGFW
policy-based mode?- AIt limits the scope of application control to the browser-based technology category only.
- BIt limits the scope of application control to scan application traffic based on application category only.
- CIt limits the scope of application control to scan application traffic using parent signatures only
- DIt limits the scope of application control to scan application traffic on DNS protocol only
22Which two statements ate true about the Security Fabric rating? (Choose two.
- AIt provides executive summaries of the four largest areas of security focus.
- BMany of the security issues can be fixed immediately by clicking Apply where available.
- CThe Security Fabric rating must be run on the root FortiGate device in the Security Fabric.
- DThe Security Fabric rating is a free service that comes bundled with alt FortiGate devices.
23The exhibits show a network diagram and the explicit web proxy configuration.
In the command diagnose sniffer packet, what filter can you use to capture the traffic between the client and the explicit web proxy?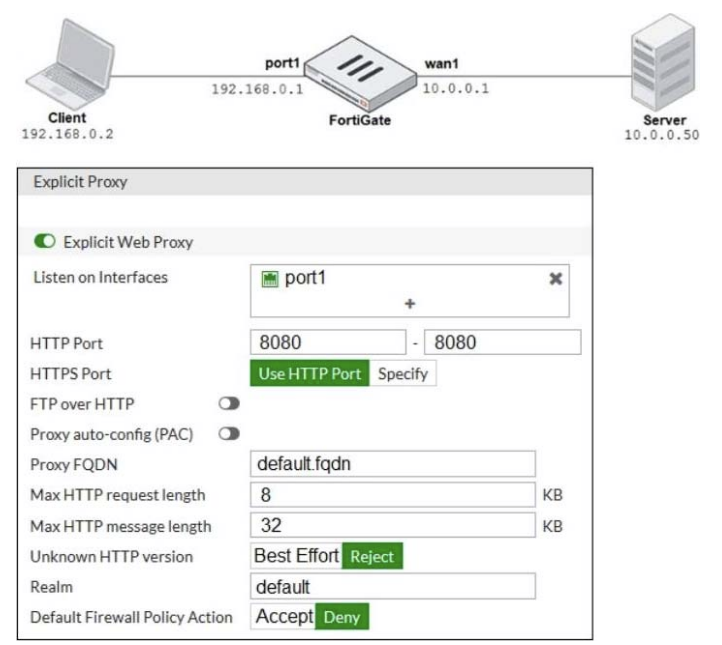
- A‘host 192.168.0.2 and port 8080’
- B‘host 10.0.0.50 and port 80’
- C‘host 192.168.0.1 and port 80’
- D‘host 10.0.0.50 and port 8080
24What inspection mode does FortiGate use if it is configured as a policy-based next-generation firewall
(NGFW)?- AFull Content inspection
- BProxy-based inspection
- CCertificate inspection
- DFlow-based inspection
25In an explicit proxy setup, where is the authentication method and database configured?
- AProxy Policy
- BAuthentication Rule
- CFirewall Policy
- DAuthentication scheme
26An administrator must disable RPF check to investigate an issue.
Which method is best suited to disable RPF without affecting features like antivirus and intrusion prevention system?- AEnable asymmetric routing, so the RPF check will be bypassed.
- BDisable the RPF check at the FortiGate interface level for the source check.
- CDisable the RPF check at the FortiGate interface level for the reply check.
- DEnable asymmetric routing at the interface level.
27When detecting attacks, which anomaly, signature, or filter will FortiGate evaluate first?
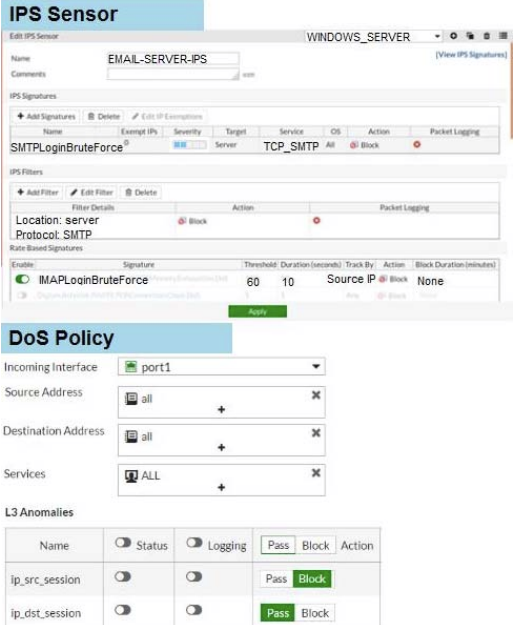
- ASMTP.Login.Brute.Force
- BIMAP.Login.brute.Force
- Cip_src_session
- DLocation: server Protocol: SMTP
28An administrator needs to configure VPN user access for multiple sites using the same soft
FortiToken. Each site has a FortiGate VPN gateway.
What must an administrator do to achieve this objective?- AThe administrator can register the same FortiToken on more than one FortiGate.
- BThe administrator must use a FortiAuthenticator device.
- CThe administrator can use a third-party radius OTP server.
- DThe administrator must use the user self-registration server.
29If the Issuer and Subject values are the same in a digital certificate, which type of entity was the certificate issued to?
- AA CRL
- BA person
- CA subordinate CA
- DA root CA
30Which of the following are purposes of NAT traversal in IPsec? (Choose two.)
- ATo detect intermediary NAT devices in the tunnel path.
- BTo dynamically change phase 1 negotiation mode aggressive mode.
- CTo encapsulation ESP packets in UDP packets using port 4500.
- DTo force a new DH exchange with each phase 2 rekey.
Information
- Description
- Ingeniería Quiz on NSE 4 2da, created by Fernando Mayorga on 01/11/2022.
- Author
- Fernando Mayorga
- Language
- Español
- Views
- 6
- History
- Created on 1 Nov 2022 · updated on 9 Nov 2022
- Tags
- Rating
- No ratings yet Rate this quiz